About Realistic Security

Founded in 2016, we're a cybersecurity team that protects organizations with practical, real-world security work.

Security That Works in Practice

Realistic Security is a cybersecurity company founded in 2016 in Algiers. Since then we have worked for more than 100 organizations, including government bodies, banks, and energy and telecom companies.
Our work covers the four stages of security. We assess with audits, penetration tests and red team exercises. We protect by designing security architectures, then deploying and integrating tools such as SIEM, EDR and firewalls. We detect with custom detection rules and compromise assessments. We respond to incidents, run the forensic investigation and monitor our clients’ systems 24/7.

Our co-founders are engineers first. Before they started the company, they worked as penetration testers, red teamers, security researchers and detection engineers.
They had seen many organizations trust controls that looked complete on paper and then failed against a real intruder. They started Realistic Security to build defenses that hold up against real attacks.

This background still shapes how we work. Every penetration test and red team engagement shows us how systems really fail. More than 10,000 hours of incident response and digital forensics show us how attacks really unfold.
We put what we learn into the detection rules we write, the architectures we design and the playbooks we hand over.
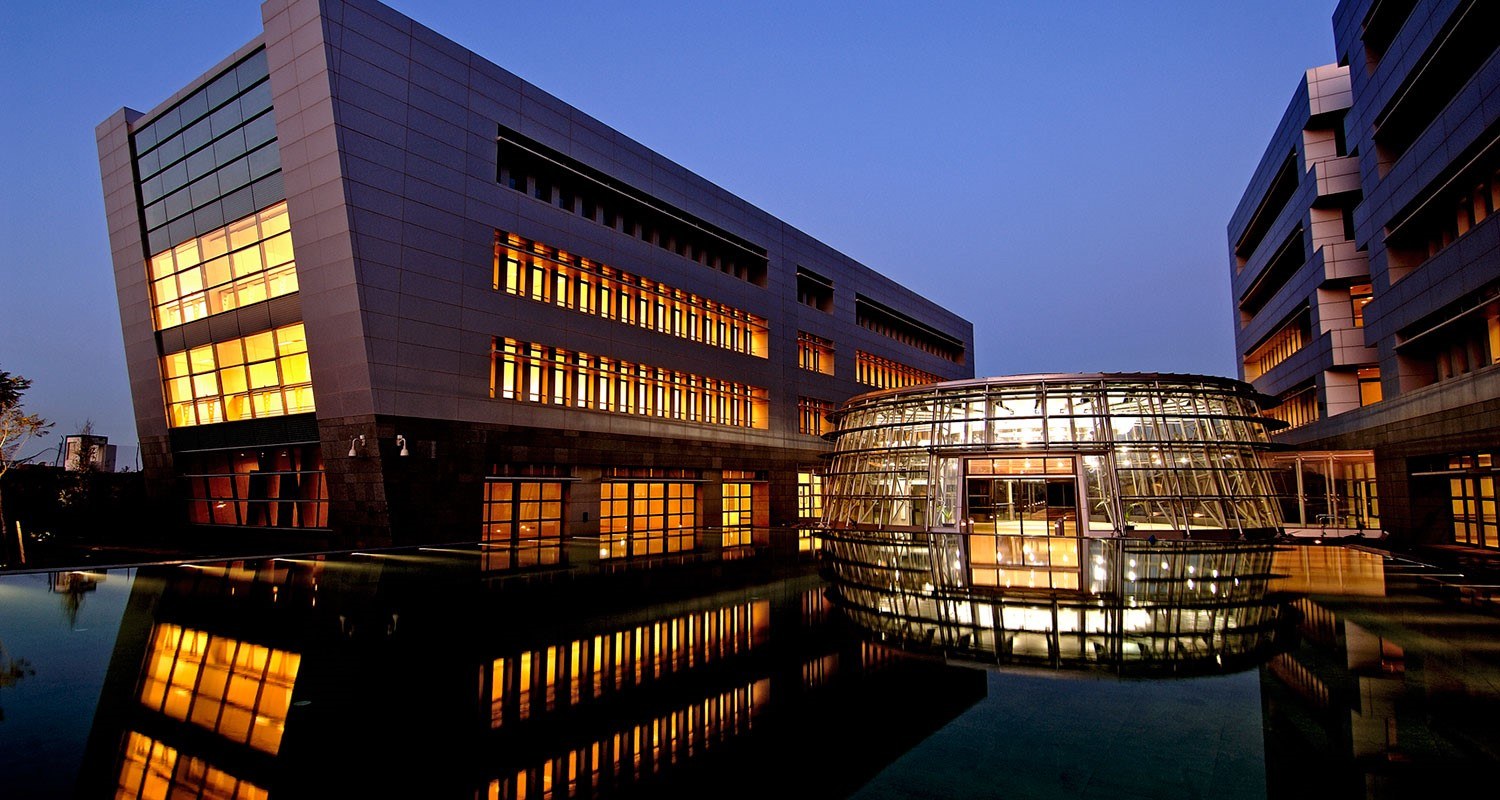
The Cyberparc Sidi Abdellah technology park in Algiers at dusk
Cyberparc Sidi Abdellah, Algiers, where Realistic Security was founded in 2016.

Our Values

The principles behind every engagement.

Realistic

We give practical advice that focuses on what matters most for your security.

Accurate

We give accurate results, with fixes your team can apply.

Simple

We keep things easy to understand and apply. Security shouldn't be complicated to implement.

Quality

Our consultants hold certifications from OffSec, Hack The Box, Cisco and other vendors. We hold every engagement to the same standard.

From Assessment to Response

We start from the challenges a CISO faces, not from a product list. Every question on the map is one we hear from security leaders, and each one leads to the service that answers it.

  1. 1. Start from your challenge

    Find the question closest to what your board, your auditors or your last incident is asking you.

  2. 2. Go to the answer

    Select it to open the service that answers it: what we do, how we deliver it and what you receive.

  3. 3. Close the loop

    Each function feeds the next: assessment shapes protection, detection tests it, and every response improves the next assessment.

01 ASSESS 02 PROTECT 03 DETECT 04 RESPOND YOUR QUESTIONS. OUR ANSWERS. Whichweaknessesshould wefix first? VulnerabilityAssessment Where can ourapps andnetwork bebroken into? Penetration Testing Can anattackerbecomedomain admin? Active DirectoryReview Is securitybuilt intoour software? Application Security Would ourcontrols stopa knownthreat actor? Adversary Emulation Could a realattackerreach ourcrown jewels? Red Teaming Is ourarchitecturebuilt fordefense indepth? SecurityArchitecture Design Are oursystems andtools properlyhardened? ControlsConfiguration Review Do we havethe rightsecuritystack? Security SolutionsDeployment Areattackersalreadyinside? CompromiseAssessment Would wedetect theirtechniques? DetectionEngineering Whichthreatsmatter mostto us? Threat Modeling We're underattack:who dowe call? IncidentResponse & DFIR Who watchesour systemsaroundthe clock? 24/7 MDR MonitoringHOSTED IN ALGERIA Is ourteam readyfor acrisis? Response Readiness Do we knowexactlywhat to do? PlaybookDevelopment

Our Experience

Field practice in building, testing and defending since 2016.

0

Years of Experience

0

Projects Delivered

0

Offensive Security Assessments

0

Hours of DFIR Operations

Team Certifications

These certifications are held by the consultants who run your engagements. Hover over or tap a logo to see which certifications we hold from it.

Ready to Work with Us?

Tell us what you need to protect. We will explain how we can help.