Web Application Testing
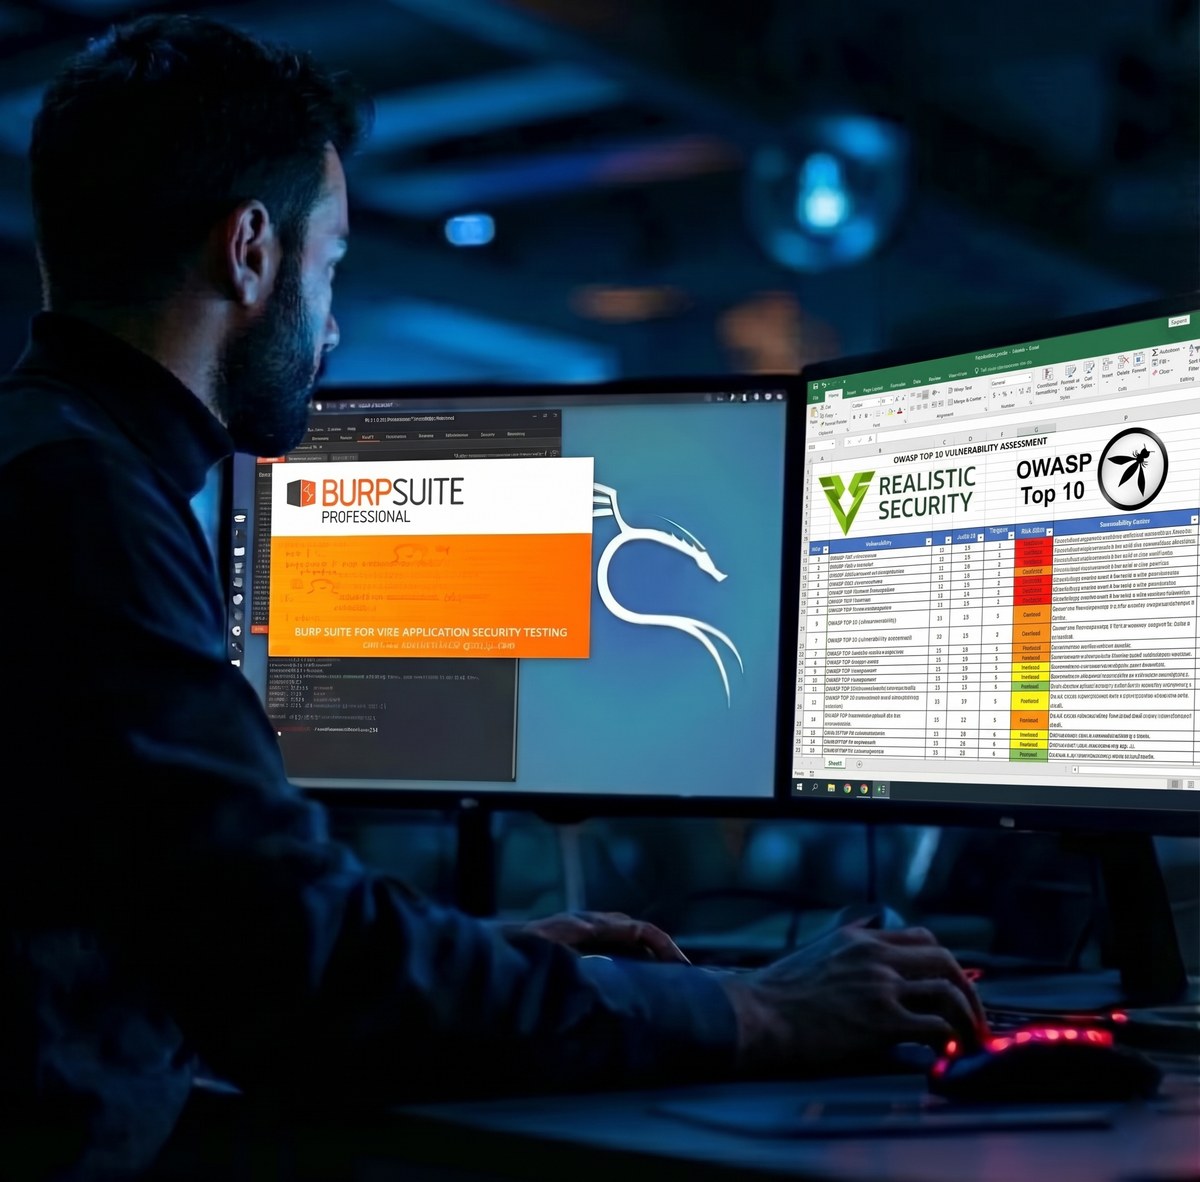
We test your web applications and APIs the way a real attacker would. Our testers work mainly by hand with Burp Suite Professional, and use automated tools only to support them.
Our web tests are built on the OWASP Top 10, the reference list of the most critical web application risks, and on the OWASP Web Security Testing Guide. We cover every Top 10 category, then go further into the business logic of your application. Every finding is mapped to its OWASP category and rated by risk.
-
OWASP Top 10 Coverage Broken access control, injection, cryptographic failures, misconfiguration and the other Top 10 risks
-
Injection & XSS SQL, command and template injection, and cross-site scripting
-
Authentication & Access Control Login bypass, weak sessions, and access to data of other users (IDOR)
-
API Security REST and GraphQL APIs tested for broken authorization and data exposure
-
Business Logic Flaws Abuse of real workflows: payments, approvals, limits and roles
Web Application Testing
Manual testing with Burp Suite, based on the OWASP Top 10.