Response Readiness

Find out if your incident response really works, before a real attacker tests it. We run realistic attack scenarios as tabletop exercises to validate your playbooks and incident response plan, and to measure how your people, processes and tools react.

What is Response Readiness?

Response Readiness is a tabletop exercise built on a realistic attack scenario. We simulate an incident step by step and inject new events as the attack unfolds. Your team responds as they would on a real day. We observe and assess every reaction: who detects, who decides, how the escalation flows, and whether the plan is followed.

Today, with AI, anyone can produce an incident response plan or a set of playbooks in a few hours. Writing the document is no longer the hard part. The hard part is knowing if it fits your organization and if it works under pressure. That needs validation by people who have handled real incidents. Our team brings more than 10,000 hours of incident response and digital forensics experience to that validation.

We also check your technical readiness: can you collect the evidence an investigation needs, and can you contain the threat fast enough?

The Strategic Question

"If we were attacked tomorrow, would our plan and our people hold up?"

A plan on paper is not readiness. Response Readiness tests your plan, your playbooks and your team against a realistic scenario, and shows you exactly where the response breaks.

Why Response Readiness Matters

  • Expert Validation: Your playbooks and IR plan, including AI-generated ones, are checked by experienced incident responders
  • Escalation Tested: See if alerts reach the right people, and if decisions are taken in time
  • Evidence Ready: Confirm you can acquire logs, disk and memory evidence when an investigation starts
  • Containment Ready: Verify you can isolate hosts and lock accounts quickly and safely
  • Compliance: Meet requirements to test your incident response capability (ISO 27001, NIST, PCI DSS)
  • Continuous Improvement: Each exercise produces a clear, prioritized list of gaps to fix before a real incident

Service details

  • Category Respond
  • Duration 2-6 weeks
  • Format Tabletop exercise + technical readiness checks
  • Deliverables Exercise Report, Gap Analysis, Improvement Roadmap
  • Frameworks NIST SP 800-61, NIST SP 800-84, ISO 27035
Request a Quote

Common Use Cases

Response readiness delivers value across various organizational needs

New or AI-Generated Playbooks

Validate playbooks and plans that were written quickly, with or without AI, before you rely on them.

Compliance Testing

Run the regular incident response test required by ISO 27001, PCI DSS and other frameworks.

Team or Tool Changes

Re-test the response after a new SOC, a new MDR provider, a merger or a change of key staff.

Annual Readiness Review

Give management clear evidence of how ready the organization is to face a major incident.

How the Exercise Works

From your documents to a tested, improved response

01

Review Plan & Playbooks

We study your incident response plan, playbooks, contact lists and escalation matrix before the exercise.

02

Design the Scenario

We build a realistic attack scenario that fits your threats and environment: ransomware, business email compromise, insider threat, cloud compromise, and more.

03

Run the Tabletop Exercise

We guide your teams through the incident and inject new events step by step, as a real attack would unfold.

04

Observe & Assess

We assess decisions, escalation, communication and timing for people and processes, and compare them to your plan.

05

Check Technical Readiness

We verify that evidence acquisition, log availability and containment actions work in practice, not only on paper.

06

Report & Roadmap

You receive a clear report with the gaps found, a corrected view of your playbooks and plan, and a prioritized improvement roadmap.

Exercise Report

After the exercise, you receive a report on how your team really responded, and what to fix first.

Executive Summary

Overall readiness level and the main gaps, written for leadership.

Exercise Timeline

Each inject, who reacted, how fast, and which decision was taken.

Plan & Playbook Gaps

Where the plan and playbooks were not followed or did not work, with corrected steps.

Improvement Roadmap

Prioritized actions for your people, processes and tools.

Response Readiness report by Realistic Security

Response Readiness in Detail

People, processes and technology, tested together

Attack Scenario Simulation

We run a tabletop exercise built on a realistic attack. The scenario is built for your sector, your threats and your technology. As the exercise moves forward, we add new events: a new alert, a ransom note, a call from a journalist, a request from a regulator.

Participants can include the SOC, IT, security management, legal, communication and executives. Everyone plays their real role, so we see how the organization responds as a whole.

  • Realistic Scenarios Ransomware, data theft, business email compromise, insider and cloud attacks
  • Live Injects New events are added step by step to test decisions under pressure
  • All Teams Involved Technical teams and business decision-makers in the same exercise
  • Timing Measured We track how long each key decision and action takes
Attack scenario and simulation preparation documents

Attack Scenario Simulation

A realistic attack, run as a tabletop exercise with your teams.
Playbook & IR Plan Validation

Your incident response plan and playbooks are tested against the scenario. We check if they are followed, if they are clear, and if they give the right answer at the right time.

This matters even more when documents were generated by AI or copied from a template. They often look complete, but miss your real teams, tools, contacts and constraints. Our experts validate them against how incidents really unfold.

  • Escalation Paths Do alerts and decisions reach the right people, in the right order?
  • Roles & Responsibilities Does everyone know who owns each decision during the incident?
  • Communication Internal, management, legal, regulator and customer communication is tested
  • Playbook Accuracy Steps that are missing, wrong or impossible to execute are identified
Playbook and incident response plan validation notes

Playbook & IR Plan Validation

Your plan and playbooks, tested against the scenario.

Technical Response Readiness

Beyond the discussion, we check if the technical response can really be done. When an incident starts, investigators need evidence, and responders need to contain the threat. We verify that both are possible in your environment.

We assess the full response chain, from detection and evidence collection to containment and recovery, and give you concrete actions to close the gaps.

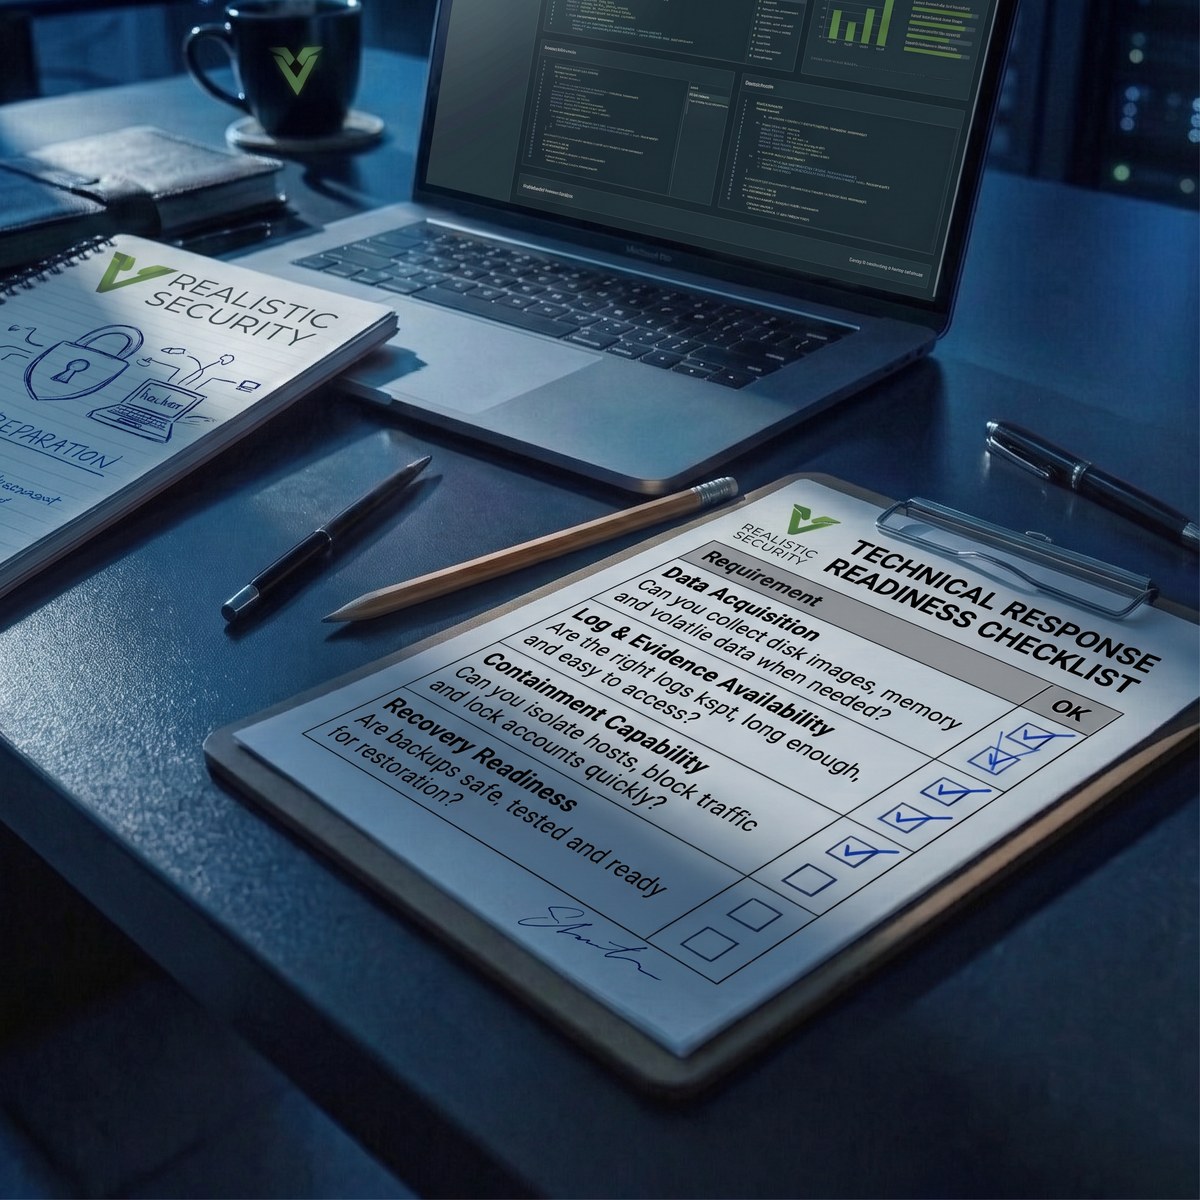
  • Data Acquisition Can you collect disk images, memory and volatile data when needed?
  • Log & Evidence Availability Are the right logs kept, long enough, and easy to access?
  • Containment Capability Can you isolate hosts, block traffic and lock accounts quickly?
  • Recovery Readiness Are backups safe, tested and ready for restoration?
Technical response readiness checklist

Technical Response Readiness

Evidence, logs, containment and recovery, checked in practice.

Ready to Test Your Response?

Get in touch with our incident response experts to plan a tabletop exercise and find out how ready your team really is.